Ransomware Incident Reconstruction: What Digital Evidence Can Actually Prove
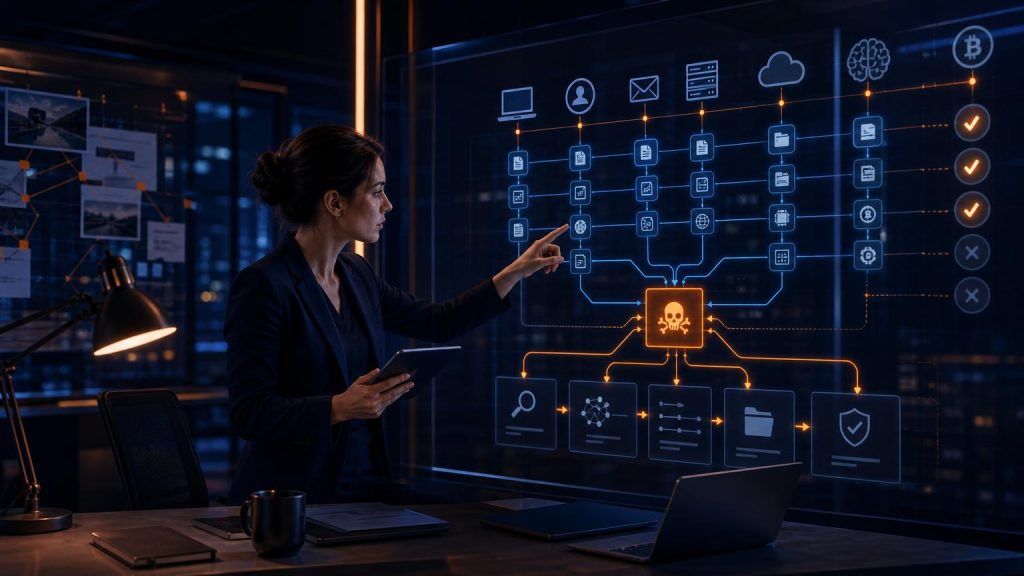
When files are encrypted, the encryption event is usually the most visible part of the incident—not the beginning of it. By that point, an attacker may already have obtained access, used legitimate credentials, moved between systems, staged data and prepared an extortion demand. The defensible question is therefore not simply when were the files encrypted? […]


