Cyber Attribution Evidence: When Technical Indicators Do Not Prove Identity
A source IP address, a familiar malware family or a match to a threat-intelligence report can make an attribution theory appear compelling. But none of those indicators, standing alone, normally answers the most consequential question: who actually conducted or directed the intrusion? The central discipline in cyber attribution is to separate technical association from identity […]
Digital Evidence Is More Than a File: A Framework for Authenticity, Integrity and Attribution
Digital evidence is often presented as though the central question were whether a file, message, log entry or database record exists. In practice, that is only the beginning. A mobile extraction, application record or cloud log may be genuine in one sense while still being insufficient to establish who created it, whether the available dataset […]
When Source Code Differs: A Defensible Method for Investigating Alleged Software Derivation
Allegations of software copying are often framed as a search for identical source code. That framing is too narrow for many real investigations. Source may have been rewritten, identifiers renamed, code obfuscated, the original repository made unavailable, or the systems made comparable only through compiled binaries and observed operation. In those circumstances, the absence of […]
Cloud Timestamps Are Not Events: Reconstructing Chronology from Digital Evidence
A cloud evidence set may contain several timestamps for what appears to be the same file or object. One may describe when a provider processed a request. Another may have been supplied by a client device. A third may have been created when an export or collection tool wrote the file to local storage. A […]
Cross-Border Electronic Evidence: How Provenance Informs Evidential Assessment
Cross-border electronic evidence rarely moves through a single, uniform process. It may be requested under an international cooperation mechanism, obtained from a service provider, transferred between investigative teams, converted into another format, translated and ultimately presented to a decision-maker in a different jurisdiction. At each stage, questions arise that are both legal and technical: who […]
When Deleted Does Not Mean Gone: Preservation Risks in Cloud and Ephemeral Messaging Systems
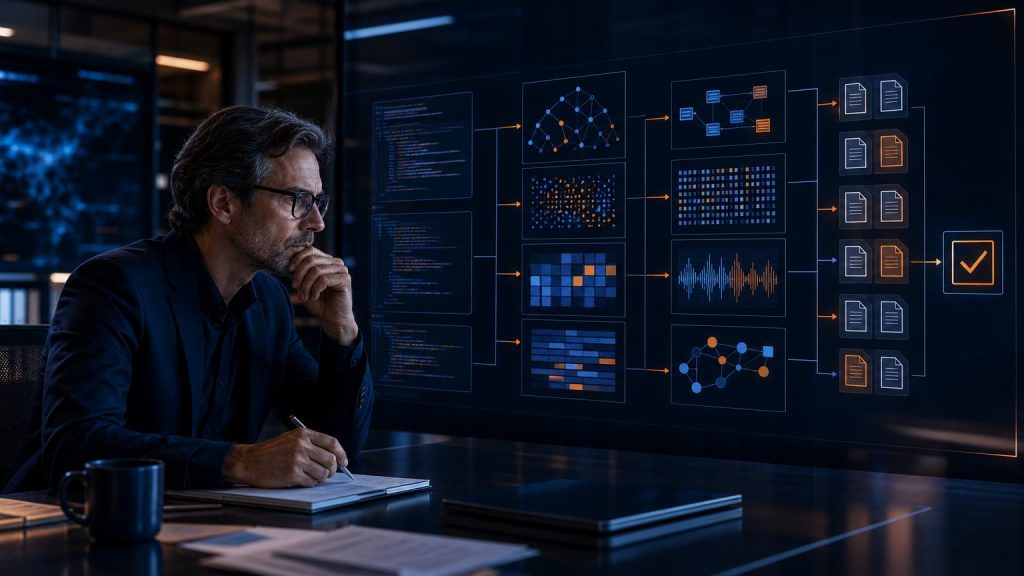
For counsel and investigations professionals, the phrase “the account was deleted” does not necessarily answer the evidentiary question. Content may have moved from a user-facing system into a deletion queue, recycle bin, versioned object store, backup or another system. Conversely, a platform may have permanently purged content, or an encrypted messaging service may never have […]
Brazil’s Electronic Voting System: What Digital Evidence Can—and Cannot—Establish
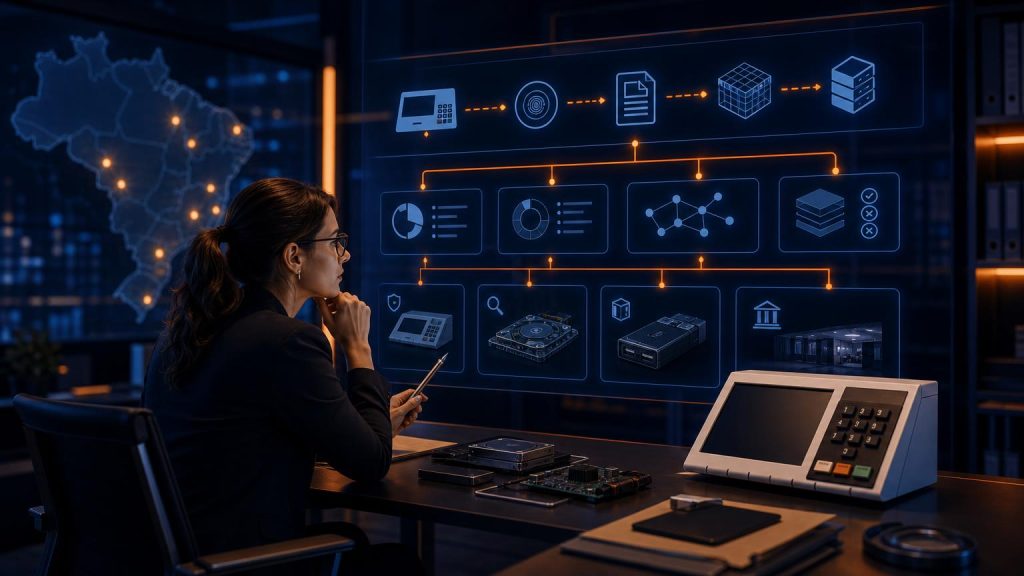
For disputes involving electronic voting, the central question is not simply whether a vulnerability exists. It is whether the available evidence can establish that the vulnerability was exploitable in the relevant environment, actually exploited during an election, and capable of changing a declared result. Those are different propositions. Treating them as interchangeable weakens both technical […]
Software Implementation Disputes: What Digital Evidence Can Establish
Software disputes often begin with a simple question: what was delivered, configured, tested or adopted, and when? The answer is rarely contained in a single contract, ticket or system log. It is usually distributed across technical environments, project records, acceptance materials and communications between the parties. A defensible assessment therefore requires more than identifying a […]
From Blockchain Address to Real-World Identity: What Cryptocurrency Evidence Can Establish
A blockchain address can appear precise. It may have a visible transaction history, a persistent balance and a sequence of incoming and outgoing transfers. Yet an address is not a name. It is a ledger identifier, and the evidential question is how, if at all, that identifier can be connected to a person or entity. […]
When Can a Cloud or SaaS Export Support a Defensible Conclusion?
A provider-issued export can appear authoritative. It may contain timestamps, account activity, messages, audit events or records of changes. In a dispute, however, the central question is not simply whether the export is intact as a file. It is what the export represents, what it does not represent, and whether another investigator could understand the […]


